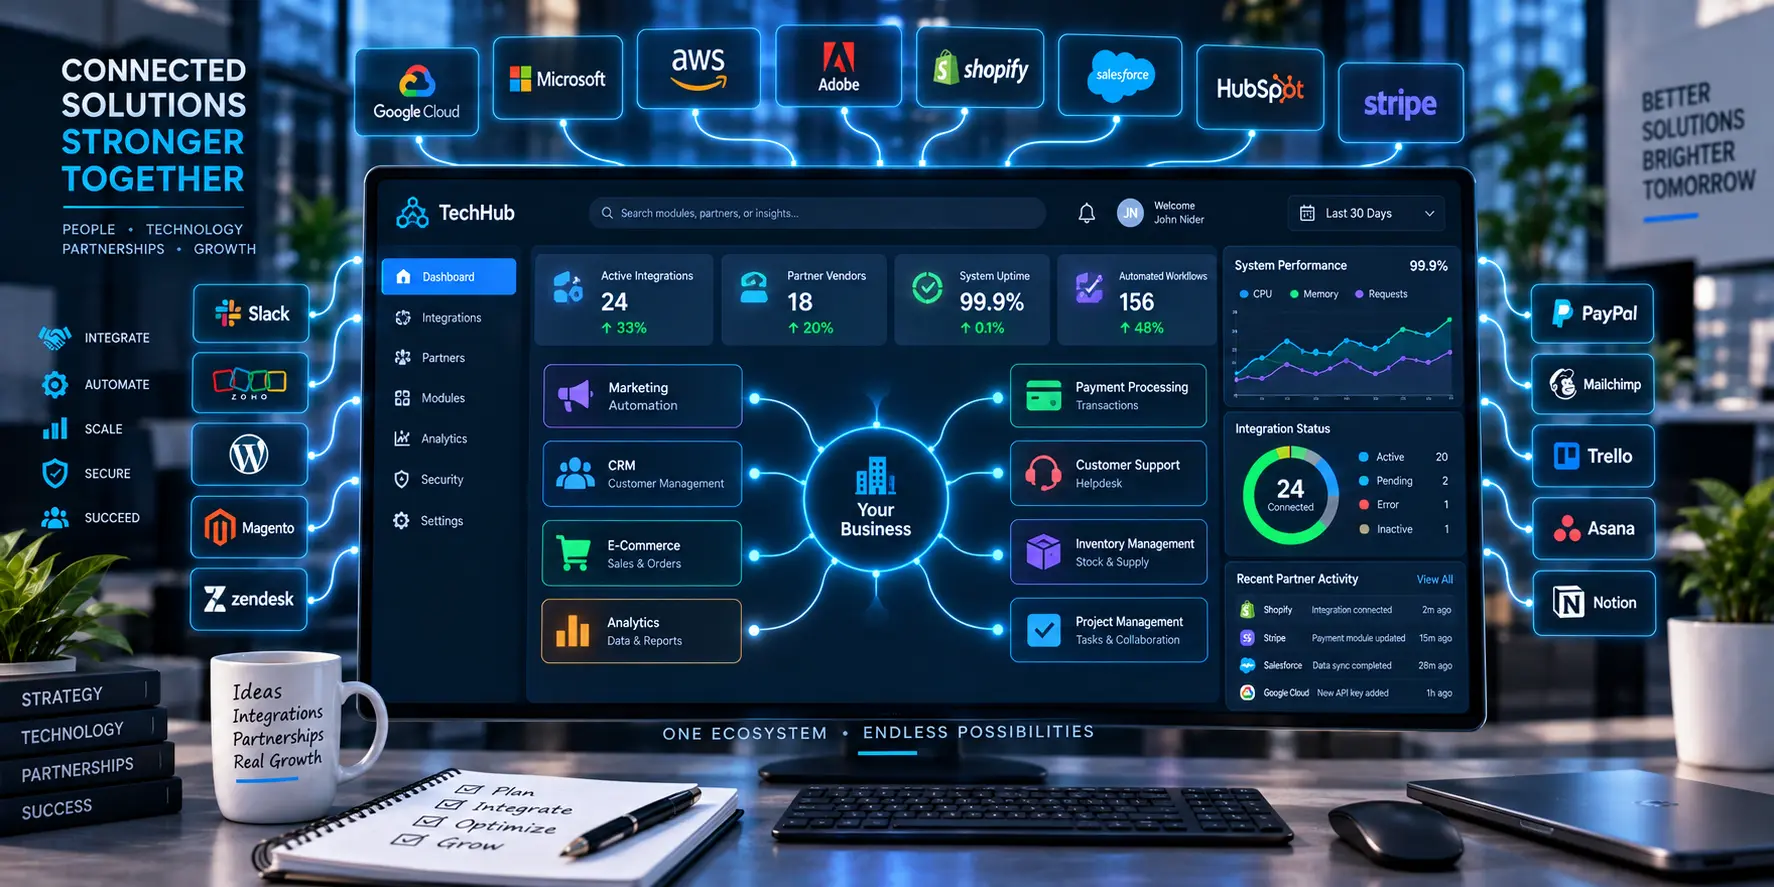
In modern software architecture, applications rarely rely on a single monolithic codebase. Instead, they operate within expansive vendor networks composed of third-party APIs, cloud infrastructure vendors, and specialized microservices. Choosing the right partners can make or break a digital product. Evaluating software provider ecosystems gives engineering leaders and CTOs the strategic framework needed to assess vendor reliability, compatibility, scalability, and long-term technical viability.
Understanding how vendor ecosystems function, why API compatibility matters, and what due diligence steps prevent integration bottlenecks allows technical teams to build resilient, future-proof platforms.
The Anatomy of Modern Tech Ecosystems
A software provider ecosystem encompasses all external tools, libraries, payment gateways, and cloud services that integrate with a core application. Rather than building every feature from scratch, modern development relies on plugging in specialized third-party services.
However, introducing external dependencies increases architectural complexity. If a provider experiences downtime, changes its API specifications without notice, or suffers a security breach, the ripple effects can destabilize the entire parent application.
Key Criteria for Vendor and Ecosystem Assessment
When comparing software providers and their surrounding ecosystems, engineering teams must look beyond marketing claims and evaluate critical operational metrics:
- API Documentation and Stability: Assessing the clarity, versioning policy, and historical uptime of a provider’s public programming interfaces.
- Security and Compliance Standards: Verifying that third-party vendors adhere to rigorous security frameworks (such as SOC 2, ISO 27001, or GDPR) to protect end-user data.
- Community and Ecosystem Support: Determining whether the provider has an active developer community, comprehensive SDKs, and responsive technical support channels.
Navigating Platform Resources and Digital Services
Managing diverse software integrations requires robust directory platforms and reliable reference tools that help engineering teams track provider updates, performance metrics, and platform compatibility standards across distributed networks.
When assessing how digital platforms aggregate third-party software resources, maintain organized service directories, and streamline technical discovery, exploring specialized informational hubs—such as checking the slot online gacor reference directory—illustrates how digital environments coordinate operational resource guides, though underlying software architectures, vendor agreements, and integration protocols vary widely across individual platforms.
Best Practices for Integrating Third-Party Services
To minimize risk and ensure smooth integration when adopting tools from external software ecosystems, technical teams should adhere to structured implementation guidelines:
- Build Modular Integration Layers: Wrap third-party API calls in abstract adapter layers so that if a vendor needs to be replaced, the change requires minimal refactoring of the core codebase.
- Implement Robust Error Handling: Design fallback mechanisms and circuit breakers to handle external service timeouts or rate-limiting errors gracefully without crashing the user interface.
- Conduct Regular Vendor Audits: Periodically review the performance, cost efficiency, and security posture of all active third-party software providers.
Common Questions About Software Ecosystems
What is a software provider ecosystem?
It is a network of interconnected software vendors, APIs, cloud services, and development tools that work together to support a core application or enterprise infrastructure.
Why is API versioning important when evaluating providers?
API versioning ensures that when a vendor updates their software backend, your application will not break unexpectedly, giving your team time to adopt new changes safely.
How do third-party integrations impact application security?
Every integrated provider introduces an additional potential attack surface. Evaluating a vendor’s security compliance and data encryption standards is crucial for maintaining overall system safety.
Conclusion
Evaluating software provider ecosystems is a vital discipline for modern technology leadership. By systematically assessing API reliability, enforcing modular integration patterns, and maintaining rigorous vendor security standards, engineering teams can build scalable, highly resilient applications that withstand shifting digital landscapes.